WEDOS Protection for Telecoms & Tier-1 Carriers

Network-Native DDoS Protection. On Your Infrastructure. Under Your Brand.

National telcos and tier-1 carriers occupy a unique position in the DDoS threat landscape. You are not just a potential target — you are the transit layer through which attacks travel to reach everyone else.

WEDOS Protection for Telecoms & Tier-1 Carriers

Built for how carrier networks actually work

That responsibility demands a protection model designed for carriers — not a cloud redirect, and not a DNS change that routes your customers' traffic to someone else's scrubbing centre in the United States.

WEDOS Protection is designed for operators who need mitigation embedded directly within their own network fabric — with the BGP engineering, on-net hardware options and commercial flexibility that carrier-grade deployments require.
Layer One

Protect your own network

Your AS, your IP ranges, your peering infrastructure and your management plane are the operational foundation your customers depend on. A volumetric attack against your own infrastructure does not affect one customer — it affects every one of them.

BGP
BGP Anycast Integration
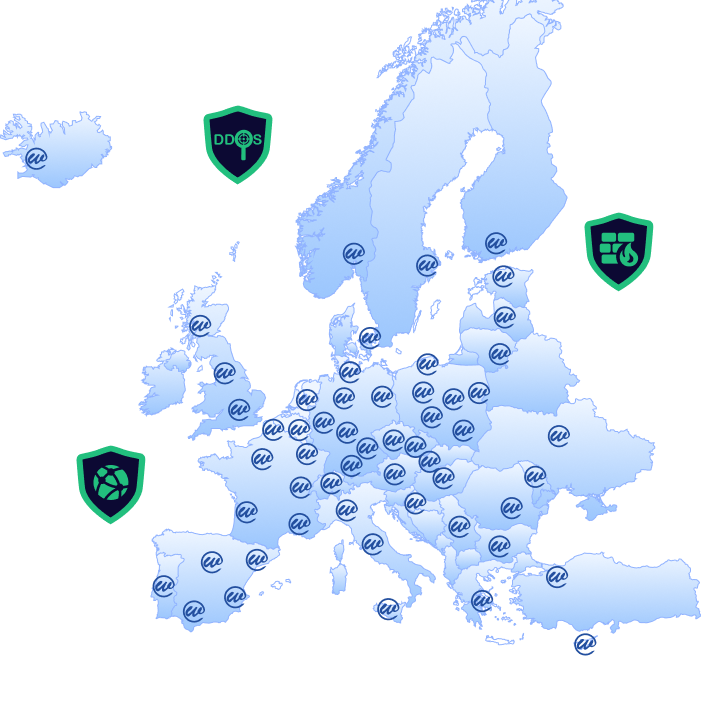
A global anycast network across 120+ PoPs with the densest European coverage among comparable providers. For tier-1 carriers, integration is via BGP peering — traffic is routed to the nearest scrubbing capacity and returned clean.
L3 / L4
Protocol & Volumetric Attack Mitigation
Full L3/L4 mitigation covering SYN, UDP and ICMP floods plus reflection and amplification via DNS, NTP and SNMP. Multi-Tbps absorption capacity, triggering automatically without NOC intervention for standard attack signatures.
L7 + WAF
L7 Application Protection
For carrier-hosted services, control platforms and customer portals: AI-driven WAF with OWASP ruleset, JA4 TLS fingerprinting, behavioural anomaly detection and per-endpoint rules. Blocks SQLi, XSS, Slowloris and HTTP floods.
NOC
Observability Built for NOC Operations
Real-time Grafana dashboards, SIEM-ready structured log export and audit-grade event logging, all within EU jurisdiction. Your NOC has full traffic visibility during an active event — not a black box reporting clean or dirty.
Layer Two

On-net PoP deployment: WEDOS hardware, your datacenter, your control

For national telcos and tier-1 operators the most powerful configuration is also the most direct: WEDOS scrubbing hardware deployed inside your own facilities and integrated via BGP peering. Not a managed service delivered from a remote location — physical infrastructure, yours to co-locate, ours to operate.

Latency
Scrubbing happens within your network, so clean traffic never traverses an external path to reach your customers. For latency-sensitive enterprise services this is a technical requirement, not a preference.
Data sovereignty
Traffic inspection and scrubbing occur on hardware physically located in your jurisdiction and your facility — decisive for operators serving regulated industries, government customers or national critical infrastructure.
Capacity ownership
On-net hardware gives you dedicated scrubbing capacity that is not shared with other customers during peak attack events. When a national-level attack occurs, your capacity is yours.
Resilience
An on-net PoP keeps operating even if connectivity to the wider anycast network is disrupted. Local scrubbing continues independently.

Deployment integrates via standard BGP peering in your datacenter environment. WEDOS engineers handle deployment, configuration and ongoing platform management, while your network team keeps traffic engineering and routing policy. For operators with requirements around data localisation, physical security or audit access, isolated hardware configurations with custom access controls are available.

Layer Three

B2B resale to your enterprise customers

Once WEDOS Protection runs on your network — via BGP anycast, an on-net PoP, or both — you have the foundation to offer DDoS protection as a managed service to your enterprise customers, under your own brand. Many of them are already evaluating standalone protection products.

White-Label Platform
Your customers see your brand, your interface, your product name. You control pricing, tier structure and the customer relationship; we provide the platform, the scrubbing capacity and the engineering.
Multi-Tenant Management
A single operator console provisions, configures and monitors protection for your entire B2B base — from a handful of enterprise accounts to thousands of business customers, with per-customer dashboards, alerting and reporting.
Tiered Service Architecture
Structure your offering across tiers — from baseline L3/L4 volumetric protection for mid-market customers to full-stack L3/L4/L7 with WAF, JA4 fingerprinting, GeoIP controls and dedicated SLA for your largest accounts.
Enterprise SLA Backing
Your customers will ask what stands behind your SLA. The answer is WEDOS's own infrastructure commitments, ISO 27001 certification, 24/7 engineering support and a platform hardened protecting hundreds of thousands of domains.
Partner Success Team
A dedicated partner success team supports technical integration, go-to-market planning, customer onboarding and escalation handling. When your sales team is closing a large enterprise deal, we are available to join the conversation.

European infrastructure, European accountability

European infrastructure, European accountability
Designed, built and operated entirely within the European Union. No hyperscaler dependency, no foreign legal exposure — every packet scrubbed and every log generated stays under EU jurisdiction.
NIS2 — the regulatory tailwind
Under NIS2, telecoms operators are essential entities with mandatory requirements for incident detection, response and reporting. The architecture — continuous monitoring, audit-grade logging, structured export — is built to support exactly that.
Built by operators, not theorists
WEDOS began as an infrastructure operator, not a security vendor. We built DDoS protection to defend our own network — hundreds of thousands of domains on one of Europe's largest hosting and DNS platforms — before offering it to anyone else.
No upstream dependency
Anycast routing, scrubbing logic, rule engine, WAF, JA4 fingerprinting, DNS protection and the management platform are all built and operated by WEDOS. No third-party scrubbing capacity, no upstream SLA to disclaim.

Three ways to deploy

BGP Anycast Integration On-Net PoP On-Net PoP + Resale
Own network protection
Scrubbing location WEDOS global PoPs Your datacenter Your datacenter
Data sovereignty EU jurisdiction Your facility Your facility
Dedicated capacity Shared platform Dedicated Dedicated
B2B resale capability Optional Optional
White-label branding
Partner success team
NIS2 documentation Included Included Included

Carriers with a network and a customer base

The telco programme is designed for national carriers and tier-1 operators with existing network infrastructure, enterprise B2B customer bases and the strategic intent to add a high-margin managed security product to their portfolio.

WEDOS Protection

Let's talk about your network.

Our carrier team will walk through BGP integration, on-net PoP options and what a resale programme looks like at your scale.