Europe's Critical Infrastructure Deserves European Protection

No foreign jurisdiction. No dependency on hyperscalers.

Your citizens trust you with their data — voter registrations, tax filings, health records, emergency services. WEDOS Protection is a DDoS protection and WAF platform designed, operated, and legally anchored exclusively in the EU.

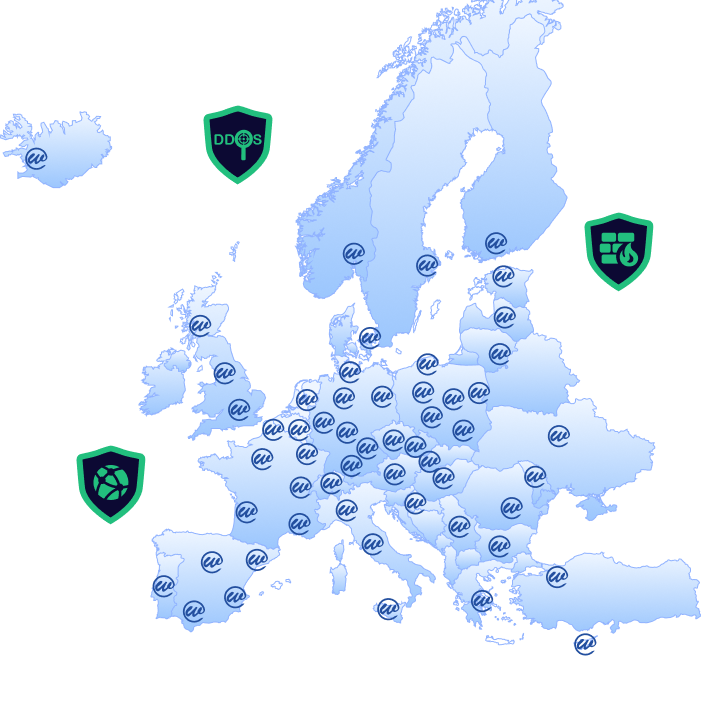
WEDOS Protection — European Points of Presence

Public services are not "just websites."

76.7% of cyber incidents targeting public institutions are DDoS attacks

76.7%
Share of cyber incidents that are DDoS attacks
targeting public administrations and governments

Governments have become the primary target for state-sponsored and hacktivist DDoS campaigns. The frequency, duration, and volume of attacks on public administration have increased sharply since 2022 — with availability attacks designed to maximise political and social impact.

Tax systems. Citizen identity. Emergency services. Election infrastructure. This is not "downtime."

  • A DDoS attack on an e-government portal means citizens cannot access services they depend on — from tax filings to emergency contacts.
  • For health or emergency portals, outages can carry life-safety implications that no SLA compensation can address after the fact.
  • Under NIS2, public administration is explicitly listed as a critical sector with binding obligations for risk management and incident reporting.
The reputational and legal consequences of a successful attack on a government portal exceed the cost of protection by orders of magnitude. Prevention is not optional — it is a legal and civic obligation.

A fully European DDoS protection and WAF platform

  • Designed, built, and operated exclusively in the European Union
  • Data never leaves EU jurisdiction — no Schrems II exposure
  • No dependency on US hyperscalers (AWS, Azure, Google Cloud)
  • Legal framework: Czech Republic, bound by EU law
  • Full auditability — source of protection is traceable and documentable
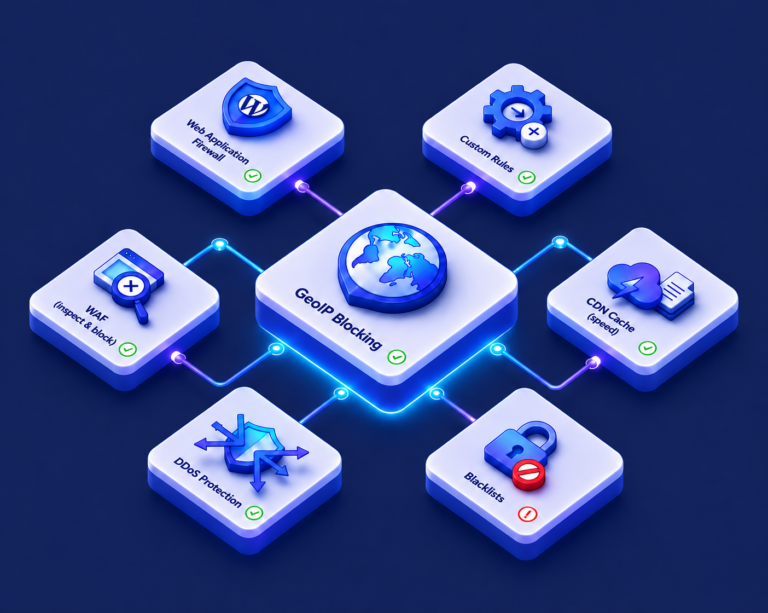
WEDOS Protection — function diagram
NIS2 compliance

Sovereignty is not a feature. It is the foundation.

  • A US CLOUD Act subpoena cannot reach WEDOS infrastructure
  • Foreign intelligence services cannot compel access to your traffic logs
  • No silent data sharing with non-EU parent companies

NIS2 Directive (EU) 2022/2555 requires that essential entities implement appropriate technical and organisational measures. WEDOS Protection is architected to support your NIS2 compliance documentation from day one.

ISO 27001
GDPR
NIS2-Ready
EU Data Centres
EU Legal Jurisdiction
24/7 Monitoring

Protection across the entire stack

Every layer of your infrastructure is covered — from raw volumetric floods to sophisticated application-layer exploits targeting government portals.

Layer 3 / 4
Network DDoS Mitigation
Absorbs volumetric floods before they reach your infrastructure — UDP floods, SYN floods, reflection amplification attacks.
  • Anycast network with 120 PoPs
  • Whole-network BGP protection, tailor-made
  • No manual intervention required
Layer 7 + WAF
Application Layer & WAF
Stops HTTP floods, credential stuffing, SQL injection, XSS, and OWASP Top 10 exploits targeting web applications and APIs.
  • OWASP Core Rule Set
  • JA4 TLS fingerprinting
  • Adaptive rate limiting
  • Custom rulesets available
Access Control
Access Control & Geo-Filtering
Define who can reach your services — by geography, ASN, IP reputation, or custom allow/deny lists for government networks.
  • Country and ASN-level filtering
  • IP reputation scoring
  • Allowlist for trusted government IPs
  • Challenge pages (JS/CAPTCHA)
DNS
DNS Protection
Anycast DNS with built-in flood mitigation protects your authoritative zones from DNS amplification and water-torture attacks.
  • Anycast DNS (WEDOS.zone)
  • DNS flood absorption
  • DNSSEC signing support
  • 100% SLA on Anycast routing
Bot Filtering
Bot Filtering
Separates legitimate citizens from automated scrapers, credential stuffers, and coordinated bot campaigns targeting public portals.
  • Behavioural analysis
  • TLS fingerprint matching
  • Good-bot allowlisting (search, monitoring)
  • Zero false positives on citizens

All traffic encrypted. All data stays in the EU.

Traffic between end users and WEDOS Protection scrubbing infrastructure is secured with TLS 1.2+ at all times. Cleaned traffic is forwarded to your origin over HTTPS or optional site-to-site VPN, so plaintext never traverses untrusted networks.

Logs and forensic data generated during mitigation are retained exclusively within European Union territory. They are available to you for incident reporting under NIS2 and for internal audits — with no third-party access without your consent.

TLS 1.2 / 1.3 HTTPS to origin VPN option Logs in EU only NIS2 incident reports

"Logs and forensic data remain fully within the European Union. No third-party access without explicit authorisation. Full chain of custody for incident documentation."

WEDOS Protection — Data Handling Policy
WEDOS Protection

The European choice for European governments

When you choose WEDOS Protection, you choose a vendor that shares your legal framework, your values, and your accountability to citizens. There are no shell companies, no offshore holding structures, no flag-of-convenience jurisdiction.
Operating since 2010 — not a startup
15+ years operating Czech and European internet infrastructure. Financial stability, long-term roadmap, no acquisition risk.
Fully EU-owned and operated
No US CLOUD Act exposure. No foreign intelligence service can compel access to your data or traffic metadata.
No hyperscaler dependency
Own physical infrastructure, own scrubbing hardware, own PoPs. Service continuity is not subject to third-party platform decisions.
Book a demo
WEDOS Protection — European Points of Presence

For government procurement teams

Everything you need to make the business case, pass the security review, and go live quickly.

Fast Activation
DNS-based onboarding — no hardware installation, no physical change. Go live within hours of contract signature.
Government SLA
100% SLA on Anycast availability. Dedicated SLA terms for public sector with enhanced incident response commitments.
Managed Onboarding
Dedicated technical account manager guides your team through configuration, testing, and go-live. No prior DDoS knowledge required.
24/7 VIP Support
Priority escalation path for critical incidents. Direct line to senior engineers — not a ticket queue — when it matters most.
NIS2 Documentation Pack
Pre-prepared documentation supporting your NIS2 risk management and incident reporting obligations. Saves weeks of compliance work.
Traffic Logging & Forensics
Detailed attack logs retained in EU. Exportable for CERT/CSIRT reporting, insurance claims, and post-incident legal proceedings.
Partnership Programme
Framework agreements available for multi-entity deployments — covering ministries, agencies, and municipal governments under a single contract.
CMS & WordPress Ready
Transparent proxy integration — compatible with any CMS, custom government portal stack, or legacy systems. No application changes required.
API & SIEM Integration
RESTful API for programmatic management. Native log export to SIEM platforms (Splunk, Microsoft Sentinel, Elastic) for your SOC team.
WEDOS Protection

Ready to protect your citizens' services?

Start with a technical demo — our team will walk you through the architecture, answer your procurement questions, and prepare a NIS2 compliance summary for your security officer.